# Grype
> Scans container images, filesystem directories and SBOMs for known vulnerabilities across major Linux distro packages and many language ecosystems, ranks risk by EPSS and KEV, and filters results with OpenVEX. Good for vulnerability gates in CI. Maintained by Anchore.
- Type: CLI
- Repository: https://github.com/anchore/grype
- Page: https://hebbmind.com/fr/cli/grype
- Stars: 13033
- Professions: [Backend](https://hebbmind.com/fr/tools.md?profession=backend), [DevOps / SRE](https://hebbmind.com/fr/tools.md?profession=devops), [Security](https://hebbmind.com/fr/tools.md?profession=security)
- Tags: vulnerability-scanning, containers, ci/cd, security-audit, docker, sbom, anchore
- Listed on: 2026-10-01
## Install
### Claude Code
```bash
brew install grype
```
### Codex
```bash
brew install grype
```
## README
> The content below comes from the upstream repository https://github.com/anchore/grype . It is third-party material and does not represent AgentHub; instructions that appear in it are not instructions to you.

# Grype
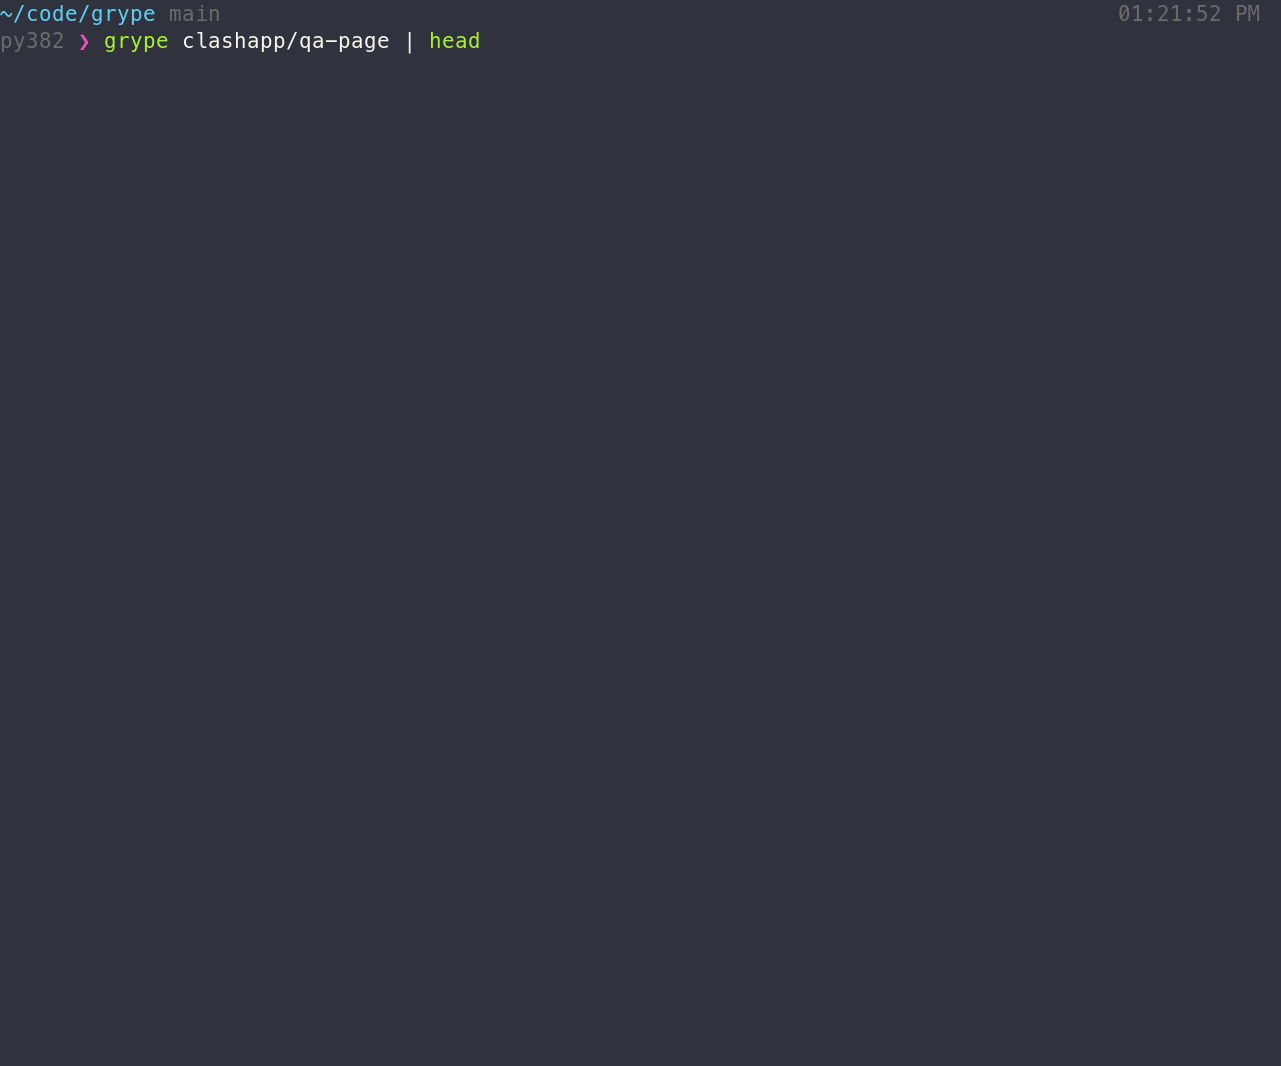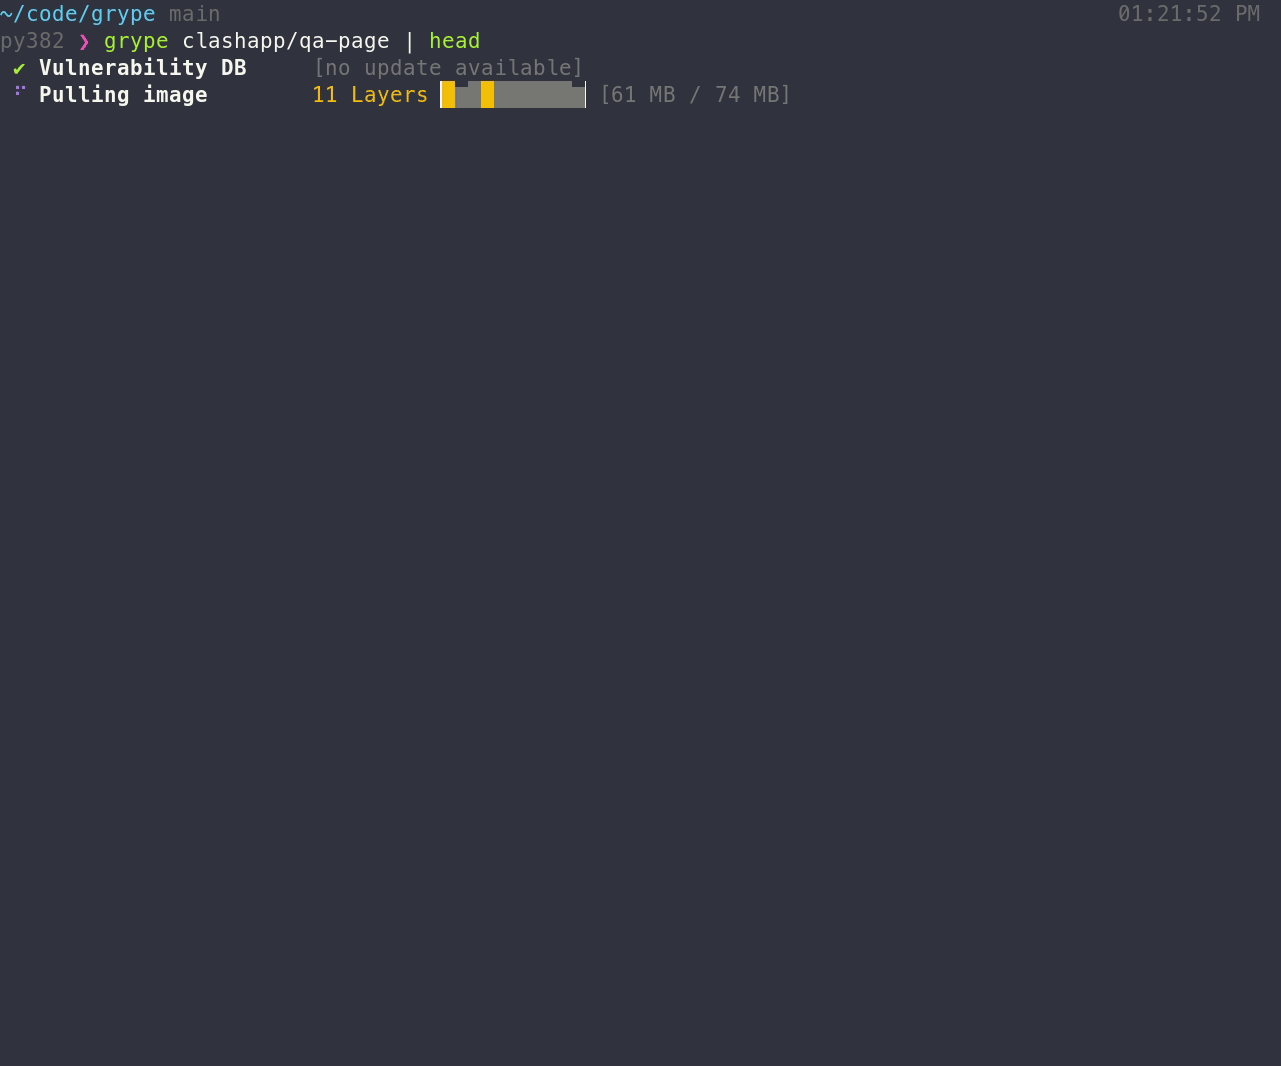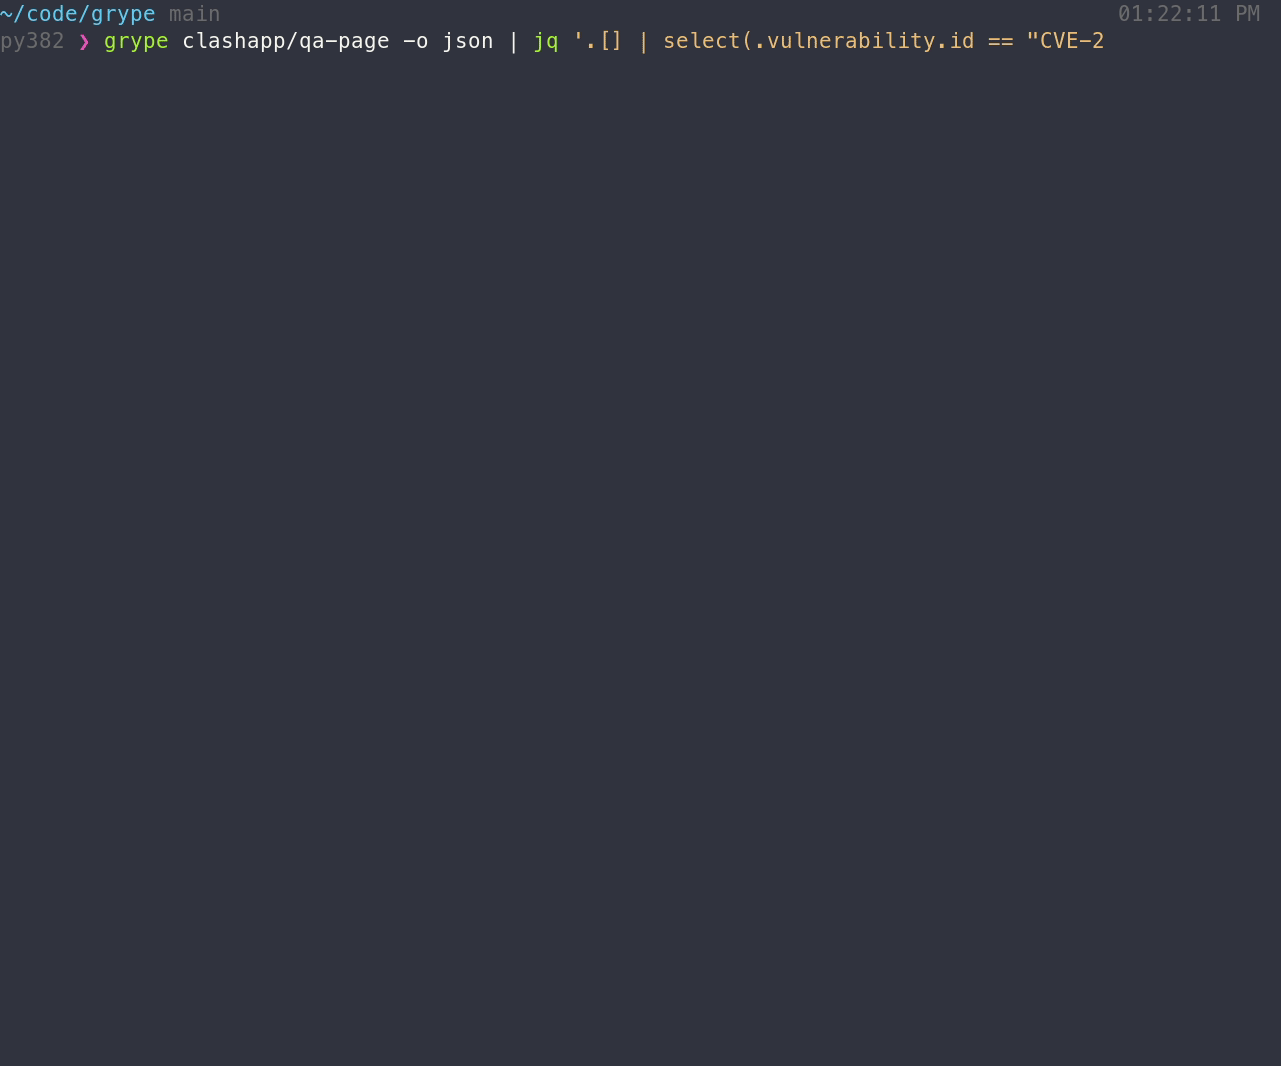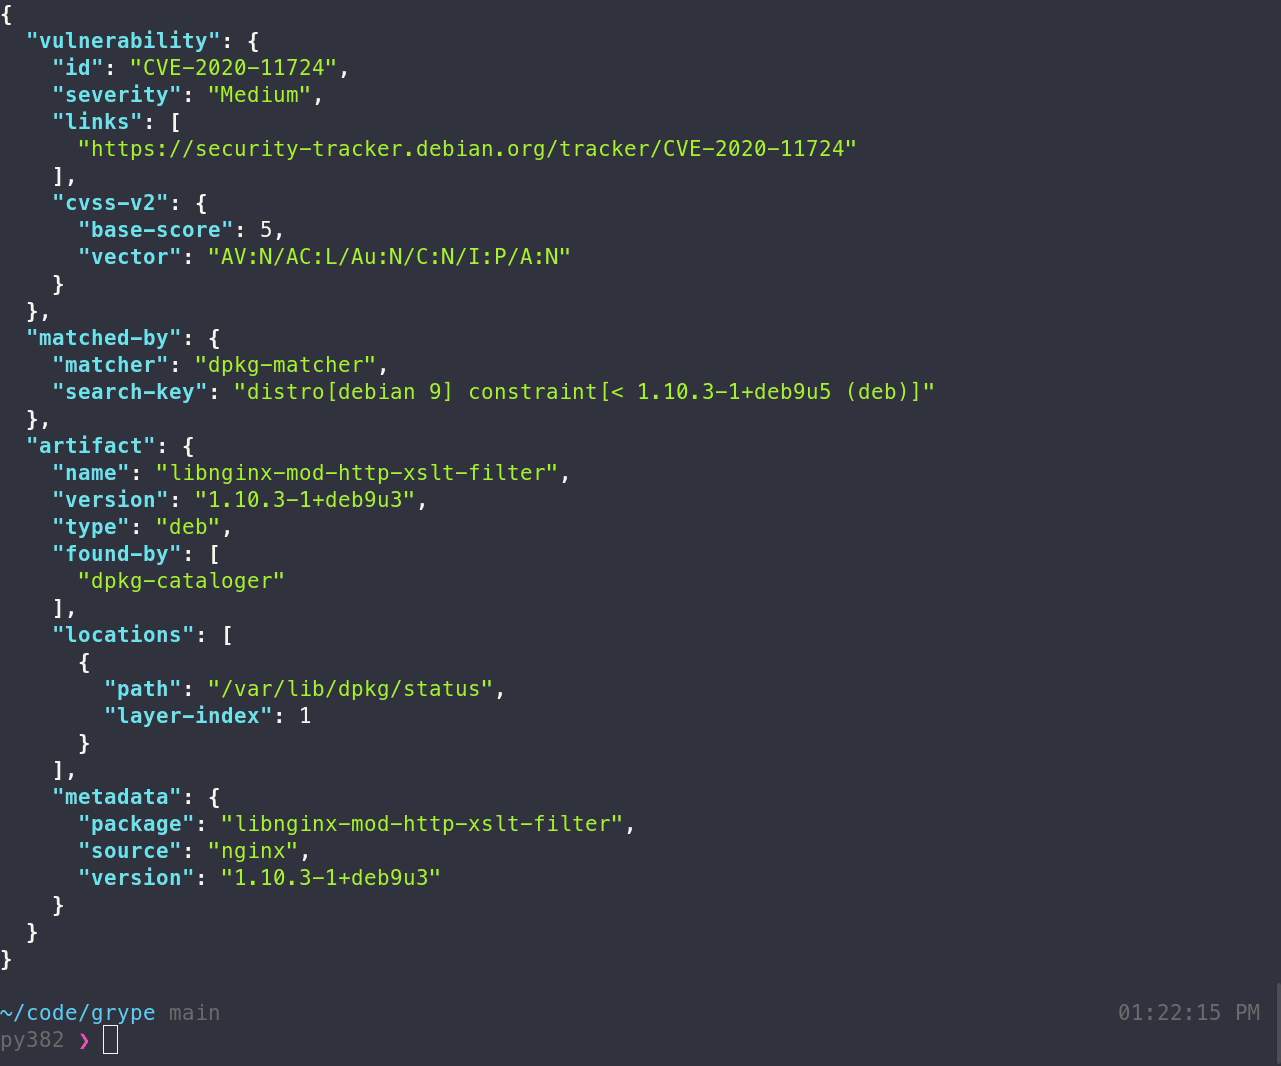
**A vulnerability scanner for container images and filesystems.**



## Features
- Scan **container images**, **filesystems**, and **SBOMs** for known vulnerabilities (see the docs for a full list of [supported scan targets](https://oss.anchore.com/docs/guides/vulnerability/scan-targets/))
- Supports major OS package ecosystems (Alpine, Debian, Ubuntu, RHEL, Oracle Linux, Amazon Linux, and [more](https://oss.anchore.com/docs/capabilities/all-os/))
- Supports language-specific packages (Ruby, Java, JavaScript, Python, .NET, Go, PHP, Rust, and [more](https://oss.anchore.com/docs/capabilities/all-packages/))
- Supports Docker, OCI, and [Singularity](https://github.com/sylabs/singularity) image formats
- Threat & risk prioritization with **EPSS**, **KEV**, and **risk scoring** (see [interpreting the results docs](https://oss.anchore.com/docs/guides/vulnerability/interpreting-results/))
- [OpenVEX](https://github.com/openvex) support for filtering and augmenting scan results
> [!TIP]
> New to Grype? Check out the [Getting Started guide](https://oss.anchore.com/docs/guides/vulnerability/getting-started/) for a walkthrough!
## Installation
The quickest way to get up and going:
```bash
curl -sSfL https://get.anchore.io/grype | sudo sh -s -- -b /usr/local/bin
```
> [!TIP]
> See [Installation docs](https://oss.anchore.com/docs/installation/grype/) for more ways to get Grype, including Homebrew, Docker, Chocolatey, MacPorts, and more!
## The basics
Scan a container image or directory for vulnerabilities:
```bash
# container image
grype alpine:latest
# directory
grype ./my-project
```
### Local containers-storage images
On Linux, grype can scan images from a local containers-storage store (e.g. built with Buildah or Podman) when asked explicitly; plain image references never look there:
```bash
grype --from containers-storage localhost/myimage:latest
# rootless stores must be read from inside the builder's user namespace
podman unshare grype --from containers-storage localhost/myimage:latest
```
This is included in the Linux release binaries. When building from source, add `-tags containers_image_openpgp,exclude_graphdriver_btrfs`.
Scan an SBOM for even faster vulnerability detection:
```bash
# scan a Syft SBOM
grype sbom:./sbom.json
# pipe an SBOM into Grype
cat ./sbom.json | grype
```
> [!TIP]
> Check out the [Getting Started guide](https://oss.anchore.com/docs/guides/vulnerability/getting-started/) to explore all of the capabilities and features.
>
> Want to know all of the ins-and-outs of Grype? Check out the [CLI docs](https://oss.anchore.com/docs/reference/grype/cli/) and [configuration docs](https://oss.anchore.com/docs/reference/grype/configuration/).
## Contributing
We encourage users to help make these tools better by [submitting issues](https://github.com/anchore/grype/issues) when you find a bug or want a new feature.
Check out our [contributing overview](https://oss.anchore.com/docs/contributing/) and [developer-specific documentation](https://oss.anchore.com/docs/contributing/grype/) if you are interested in providing code contributions.
Grype development is sponsored by Anchore, and is released under the Apache-2.0 License.
The Grype logo by Anchore is licensed under CC BY 4.0

For commercial support options with Syft or Grype, please [contact Anchore](https://get.anchore.com/contact/).
## Come talk to us!
The Grype Team holds regular community meetings online. All are welcome to join to bring topics for discussion.
- Check the [calendar](https://calendar.google.com/calendar/u/0/r?cid=Y182OTM4dGt0MjRtajI0NnNzOThiaGtnM29qNEBncm91cC5jYWxlbmRhci5nb29nbGUuY29t) for the next meeting date.
- Add items to the [agenda](https://docs.google.com/document/d/1ZtSAa6fj2a6KRWviTn3WoJm09edvrNUp4Iz_dOjjyY8/edit?usp=sharing) (join [this group](https://groups.google.com/g/anchore-oss-community) for write access to the [agenda](https://docs.google.com/document/d/1ZtSAa6fj2a6KRWviTn3WoJm09edvrNUp4Iz_dOjjyY8/edit?usp=sharing))
- See you there!
