
zizmor
CLICI/CD 配置的安全静态分析工具:找出 GitHub Actions 工作流中的模板注入、凭据泄露、权限过大等问题,也覆盖 Dependabot 与 pre-commit 配置,部分问题可自动修复。
🌈 zizmor




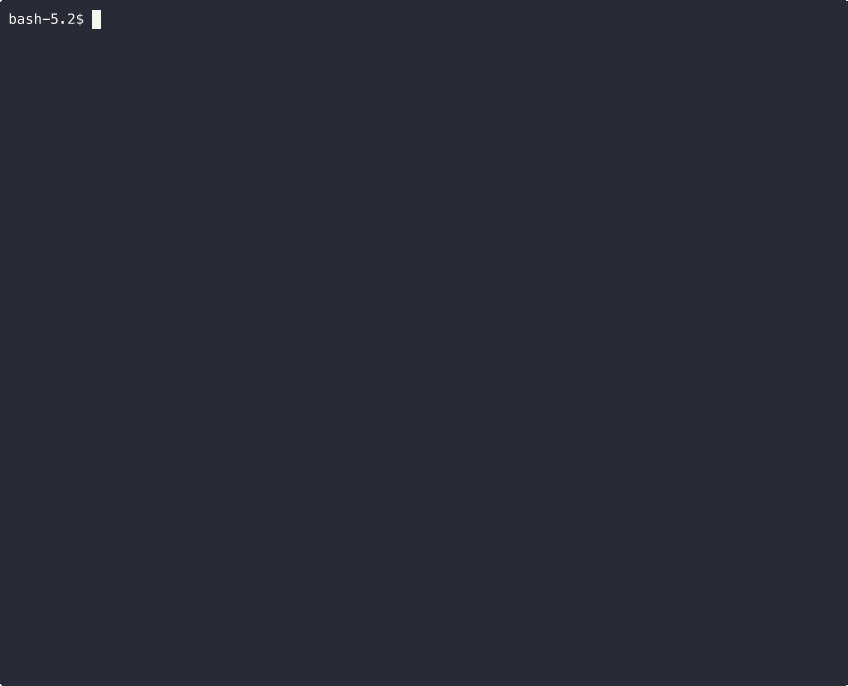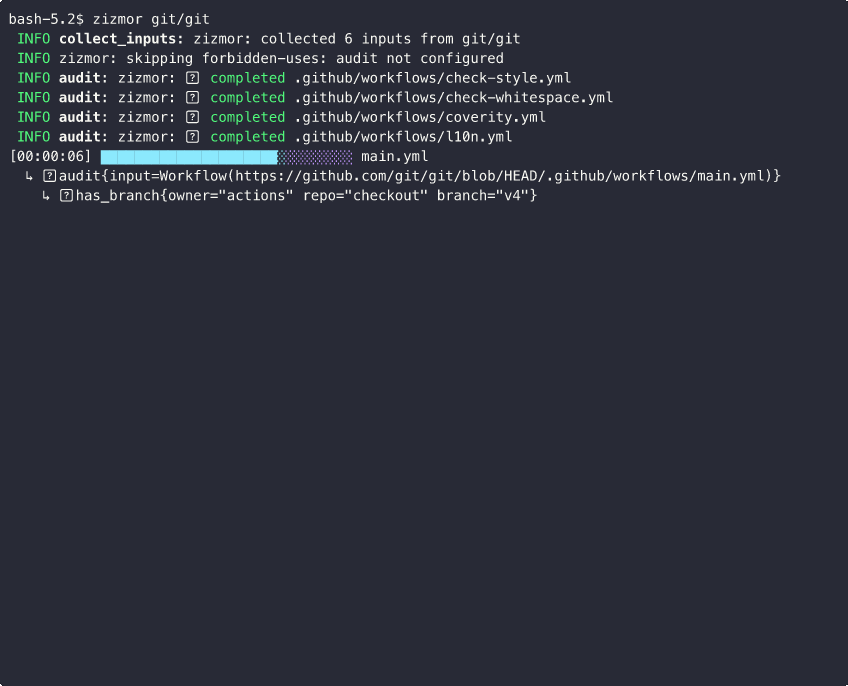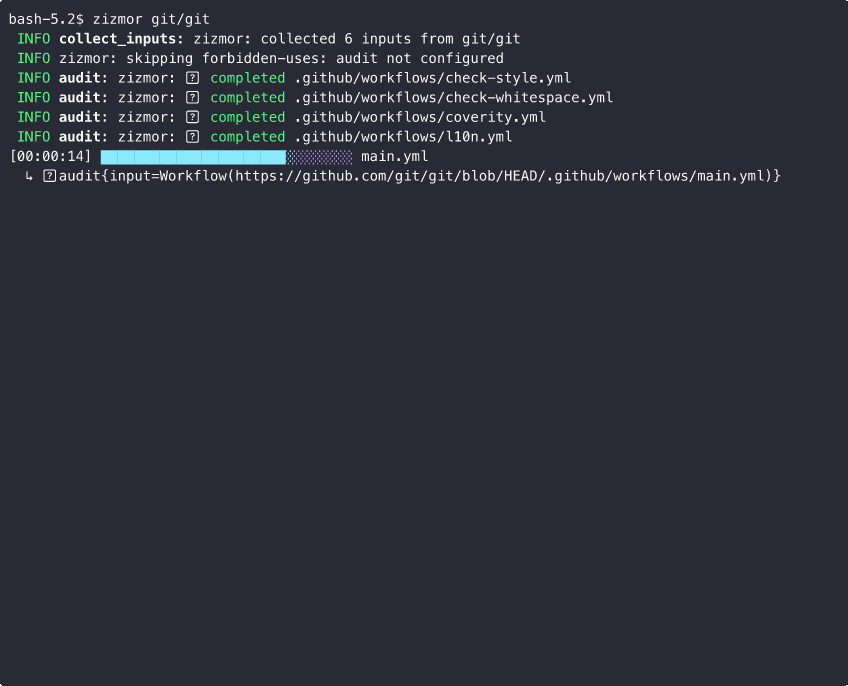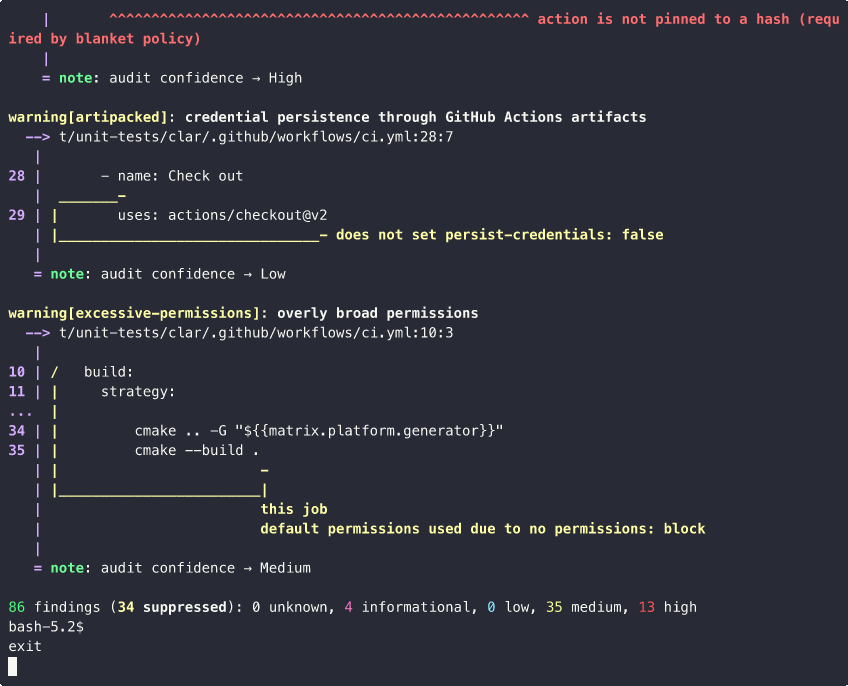
zizmor is a static analysis tool for CI/CD systems.
It can find and fix security issues in common CI/CD setups, including GitHub Actions,
Dependabot, and pre-commit. Some of the things zizmor finds:
- Template injection vulnerabilities, leading to attacker-controlled code execution
- Accidental credential persistence and leakage
- Excessive permission scopes and credential grants to runners
- Impostor commits and confusable
gitreferences - ...and much more!
See zizmor's documentation
for installation steps, as well as a quickstart and
detailed usage recipes.
License
zizmor is licensed under the MIT License.
Contributing
The name?
Now you can have beautiful clean workflows!
Sponsors
zizmor's development is supported by these amazing sponsors!

Grafana Labs |

Trail of Bits |

Kusari |

Tracebit | ||||

Coder |

glueckkanja AG |

prospex | |||||
| Alexander Riccio | Carol Willing |
Want to see your name or logo above? Consider becoming a sponsor through one of the following:
- GitHub Sponsors (preferred)
- thanks.dev
- ko-fi
Star History
相關資源

act
CLI在本地用 Docker 运行 GitHub Actions 工作流,改完 .github/workflows 不必反复提交推送就能验证 CI,也能把工作流当作本地任务运行器。需要本机安装 Docker。
nektos/act72.4k
GitHub Agentic Workflows
CLIGitHub 官方 gh 扩展:用 Markdown 编写由 AI agent 执行的 Actions 工作流并编译为标准 Actions,可选 Copilot、Claude Code、Codex 等引擎,默认只读沙箱运行。需先安装 gh。
github/gh-aw5.4k
TruffleHog
CLI在 Git、GitHub、S3、文件系统等来源中查找泄露的凭据,可识别 800 多种密钥类型,并登录对应服务验证密钥是否仍然有效,减少误报。
trufflesecurity/trufflehog28.6k
Agentic Actions Auditor
SkillTrail of Bits 出品的技能:审计接入 AI 编码 agent(Claude Code Action、Codex、Gemini CLI 等)的 GitHub Actions 工作流,检测提示注入、env 变量中转、危险沙箱配置与通配符 allowlist 等越权风险。
trailofbits/skills7.6k
GitHub CLI
CLIGitHub 官方命令行:在终端里管理 PR、Issue、Release 与 Actions 工作流,多数命令支持 --json 输出便于 agent 解析,并提供官方 agent skill。需先 gh auth login 登录。
cli/cli46.7k
Semgrep
CLI语义化的多语言静态分析工具:用写法接近源码的规则查找漏洞与缺陷,支持 30 多种语言与自定义规则,默认在本地扫描、不上传代码。跨文件分析与 Pro 规则需登录。
semgrep/semgrep17.1k