
promptfoo
CLI评测与红队测试大模型应用的 CLI 与库:批量对比提示词与模型输出、扫描安全漏洞、接入 CI/CD,评测在本地运行。已并入 OpenAI,仍以 MIT 协议开源。
Promptfoo: LLM evals & red teaming


promptfoo is a CLI and library for evaluating and red-teaming LLM-based apps. Stop using trial-and-error... start shipping secure, reliable agents
Website · Getting Started · Red Teaming · Documentation · Discord
Promptfoo is now part of OpenAI. Promptfoo remains open source and MIT licensed. Read the company update.
Quick Start
npm install -g promptfoo
promptfoo init --example getting-started
Also available via brew install promptfoo and pip install promptfoo. Or use npx promptfoo@latest to run any command without installing.
Most LLM providers require an API key. Set yours as an environment variable:
export OPENAI_API_KEY=sk-abc123
Run an eval and view results:
cd getting-started
promptfoo eval
promptfoo view
See Getting Started (evals) or Red Teaming (vulnerability scanning) for more!
What can you do with Promptfoo?
- Test your prompts and models with automated evaluations
- Secure your LLM apps with red teaming and vulnerability scanning
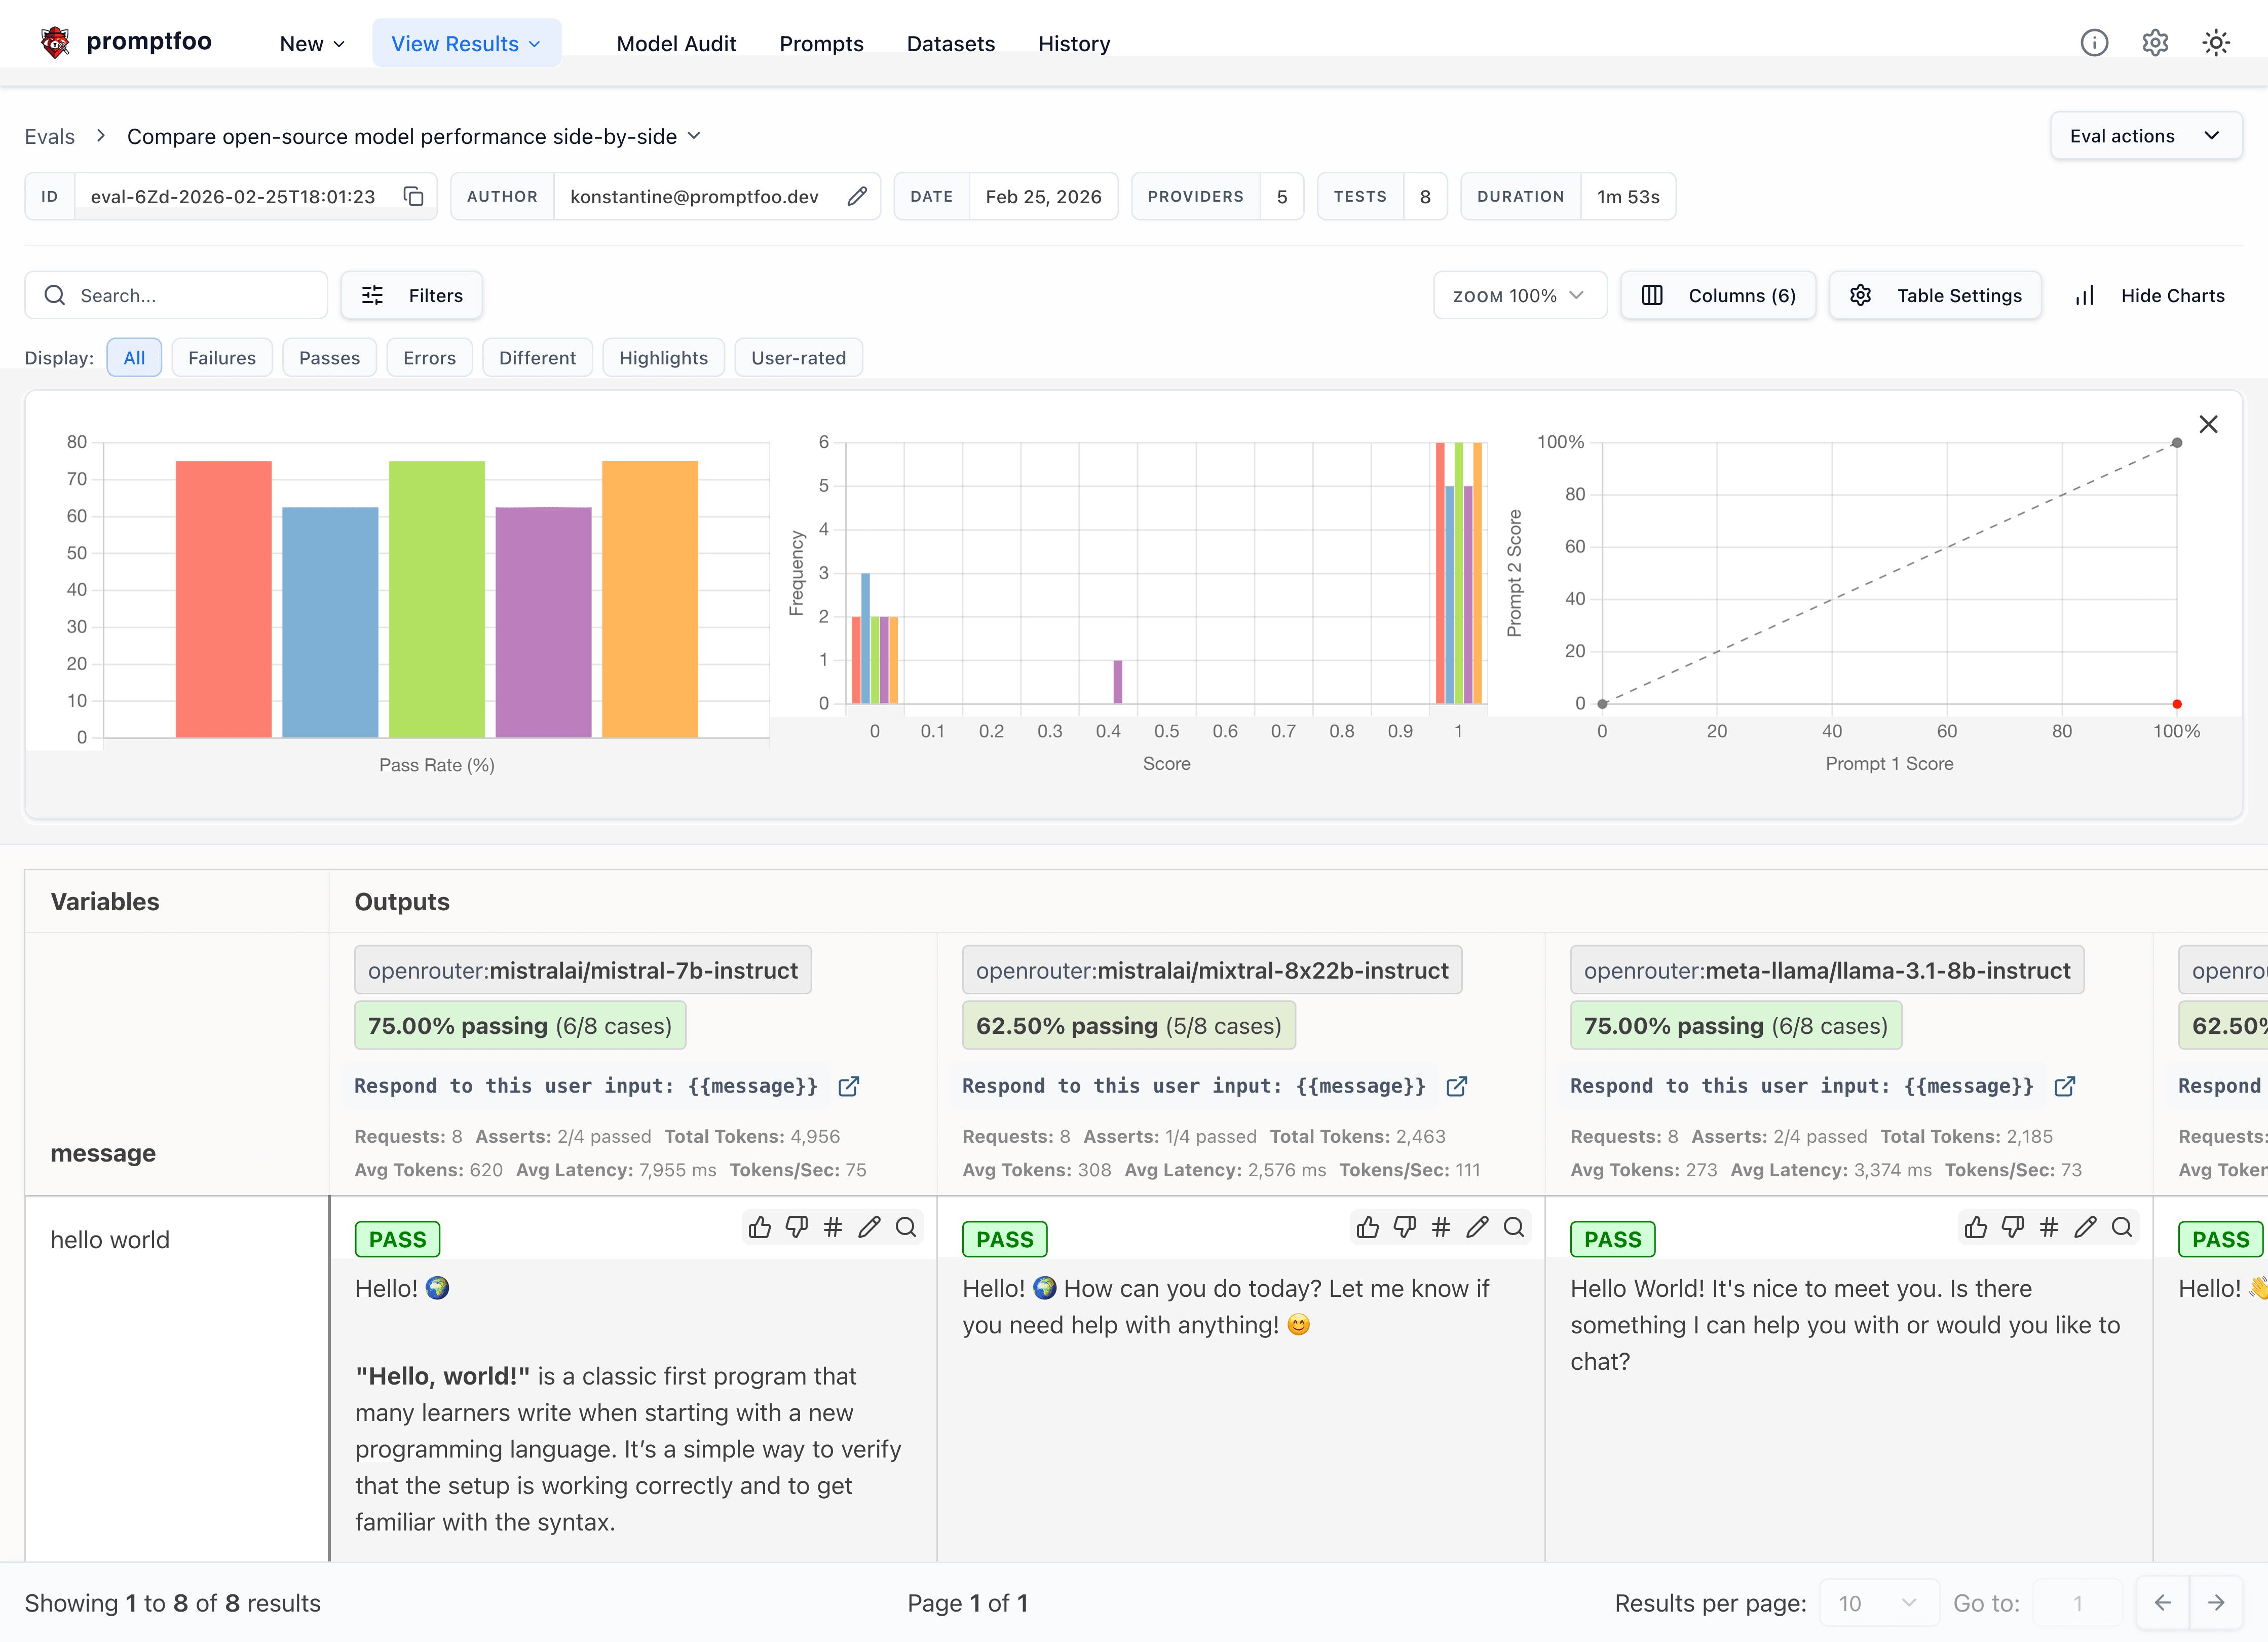
- Compare models side-by-side (OpenAI, Anthropic, Azure, Bedrock, Ollama, and more)
- Automate checks in CI/CD
- Review pull requests for LLM-related security and compliance issues with code scanning
- Share results with your team
Here's what it looks like in action:
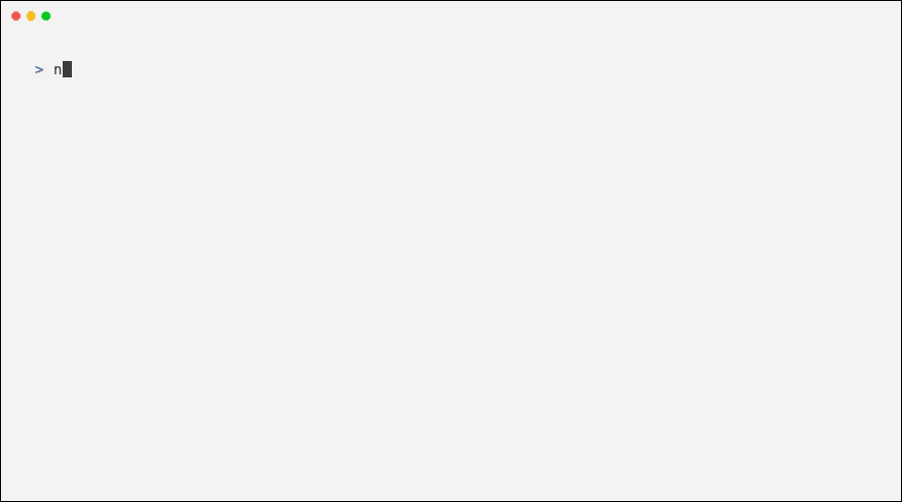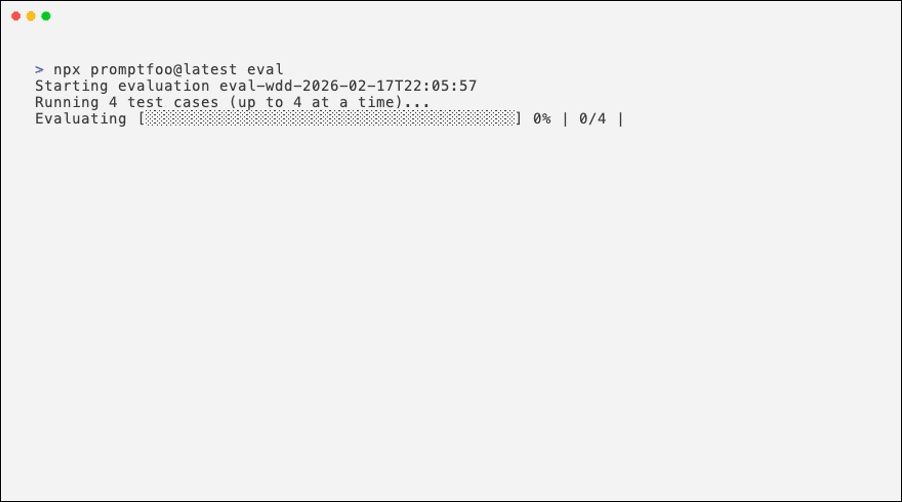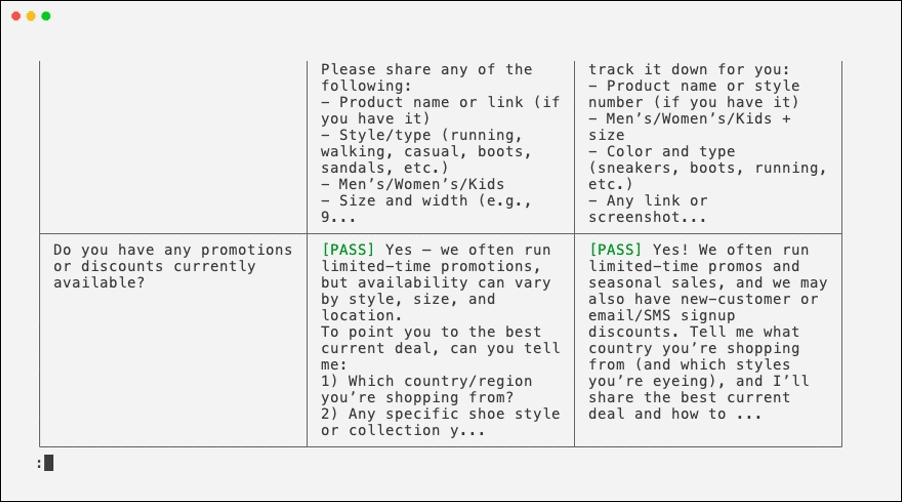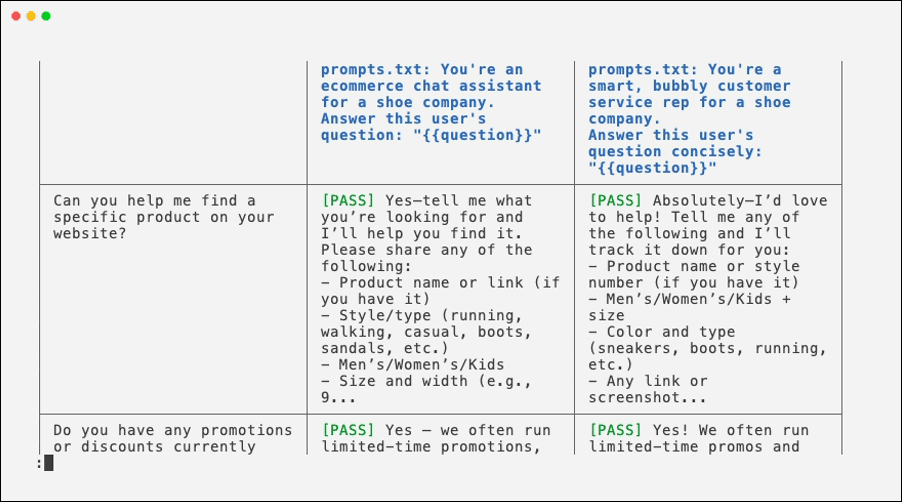
It works on the command line too:
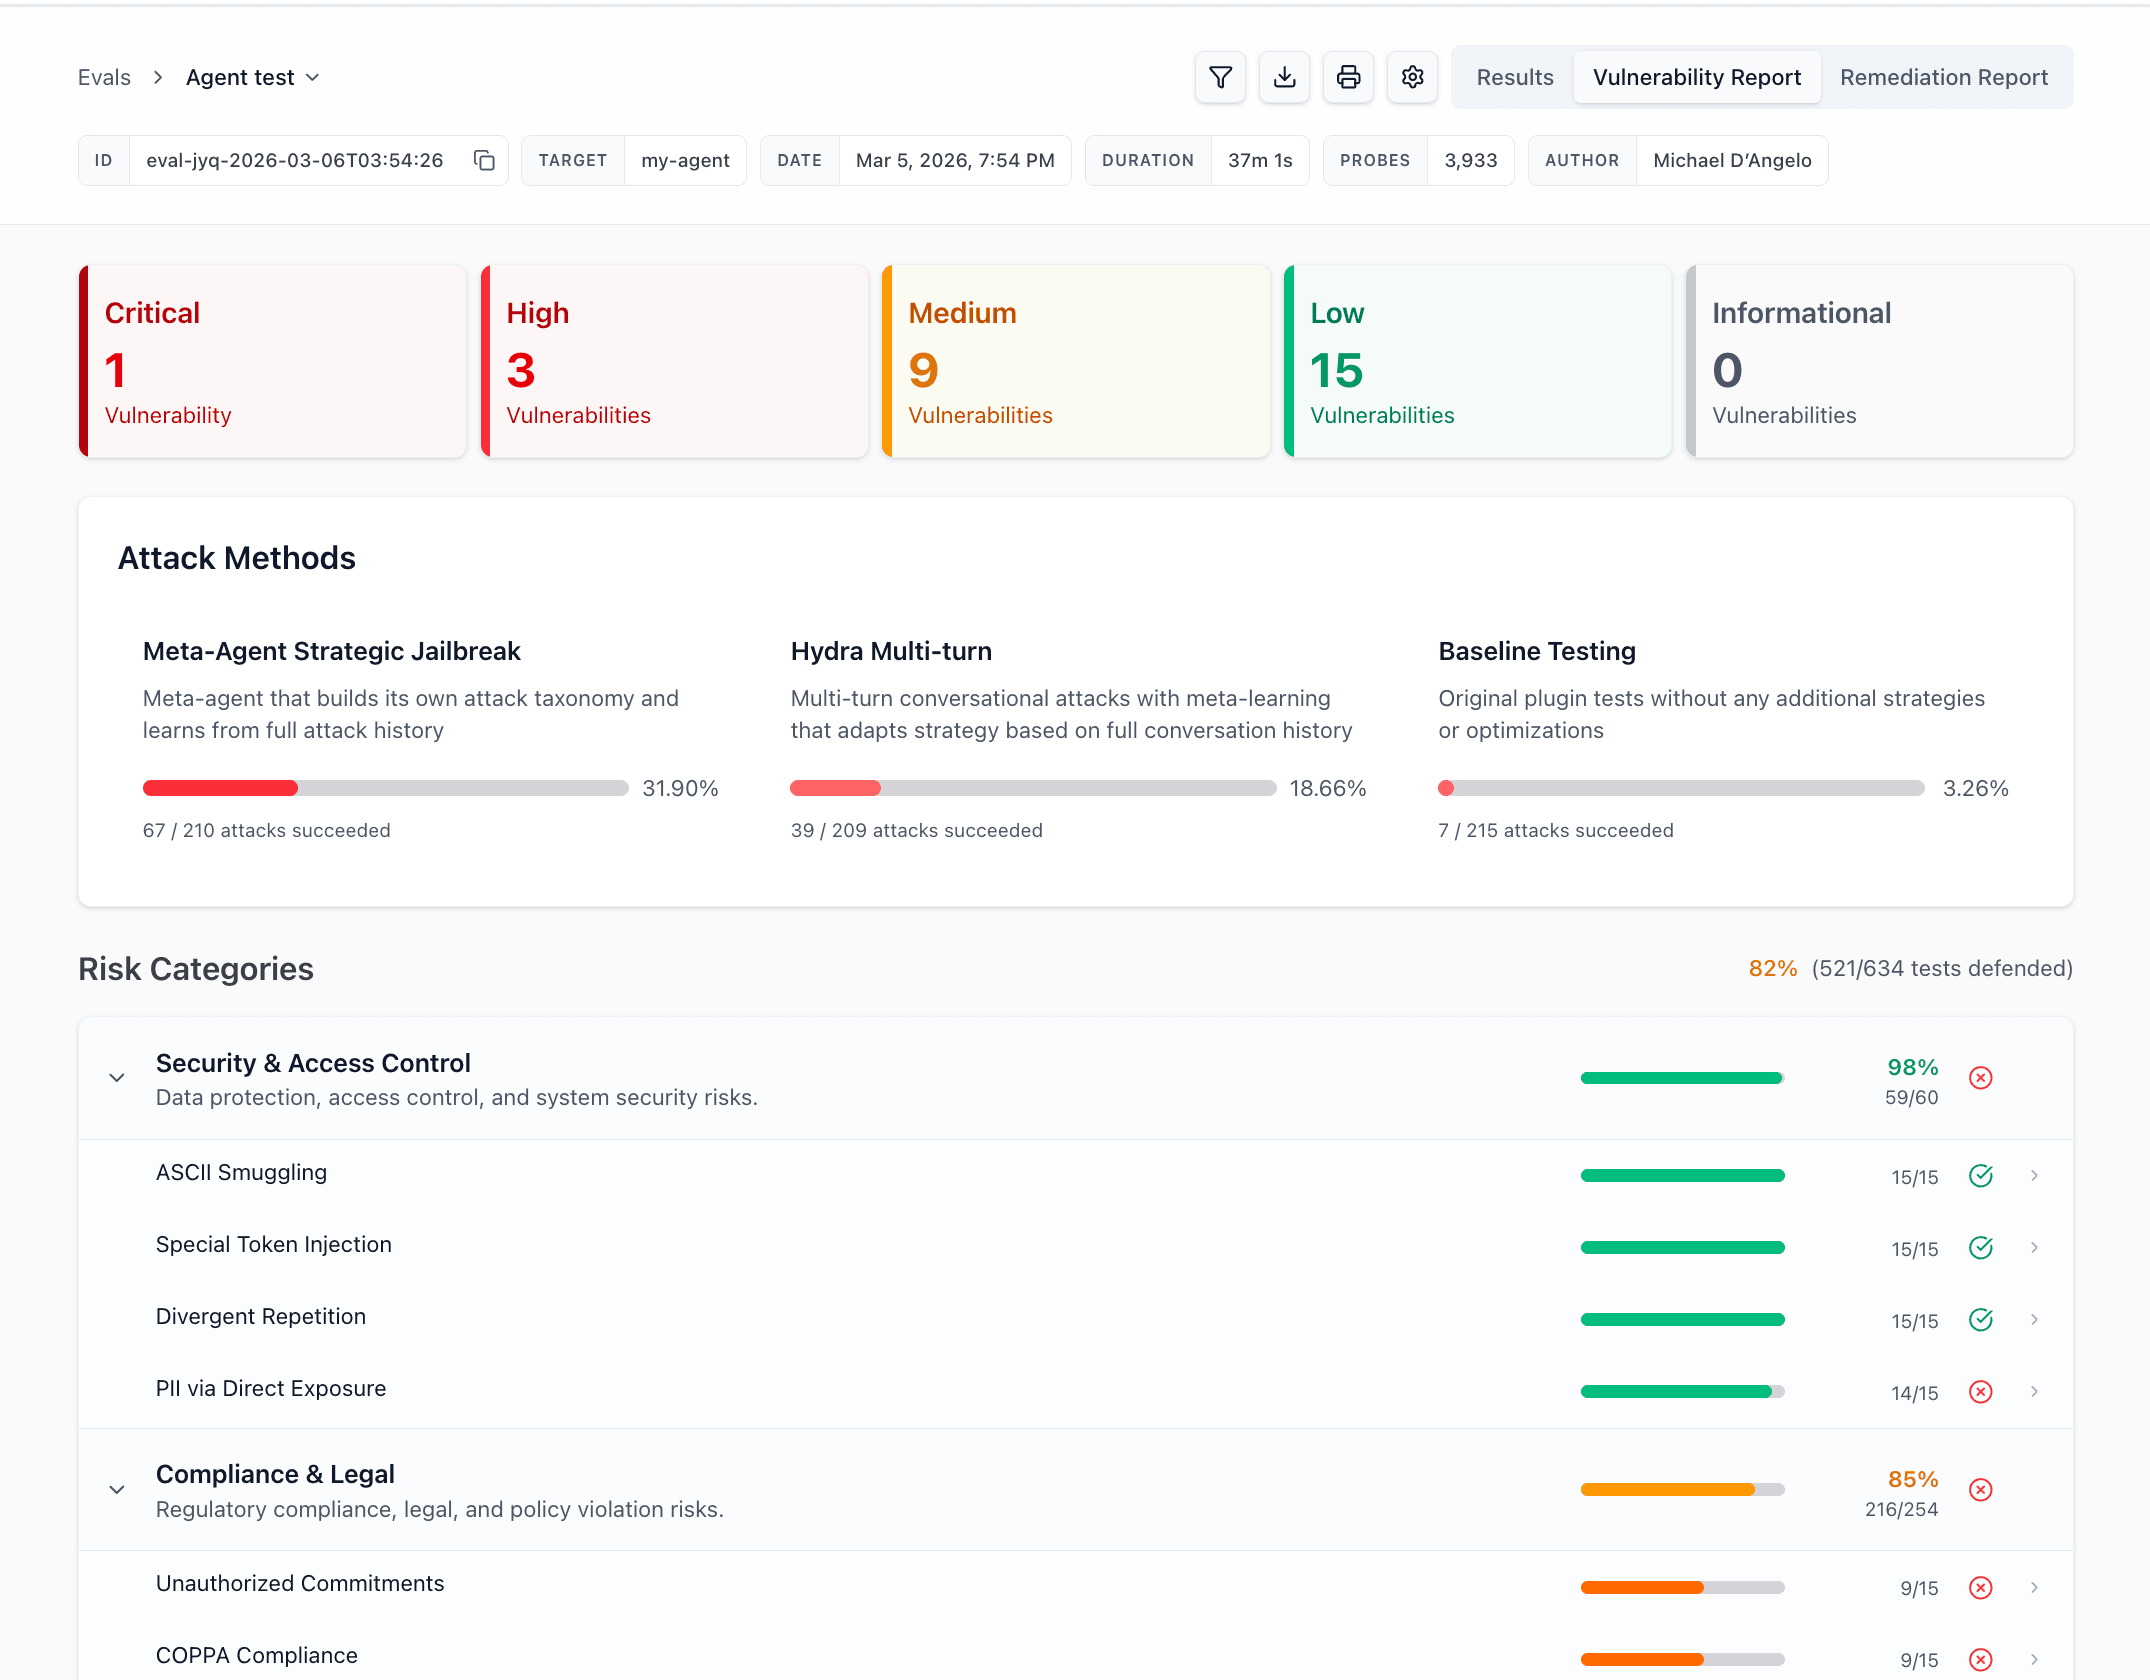
It also can generate security vulnerability reports:
Why Promptfoo?
- Developer-first: Fast, with features like live reload and caching
- Private: LLM evals run 100% locally - your prompts never leave your machine
- Flexible: Works with any LLM API or programming language
- Battle-tested: Powers LLM apps serving 10M+ users in production
- Data-driven: Make decisions based on metrics, not gut feel
- Open source: MIT licensed, with an active community
Learn More
- Getting Started
- Full Documentation
- Red Teaming Guide
- CLI Usage
- Node.js Package
- Supported Models
- Code Scanning Guide
Contributing
We welcome contributions! Check out our contributing guide to get started.
Join our Discord community for help and discussion.
相关资源

Arize Phoenix MCP Server
MCP连接 Arize Phoenix 可观测平台,让 agent 查询 LLM 调用追踪与会话、管理提示词、浏览数据集并读取实验评测结果。Arize 官方维护,需要自建或云端的 Phoenix 实例。
Arize-ai/phoenix11.9k
garak
CLINVIDIA 官方开源的大模型漏洞扫描器,探测提示注入、越狱、数据泄露、幻觉和有害内容等弱点,支持 OpenAI、Hugging Face、Bedrock 以及多数可经 REST 访问的模型。扫描云端模型时需要对应的 API Key。
NVIDIA/garak9.6k
Semgrep
CLI语义化的多语言静态分析工具:用写法接近源码的规则查找漏洞与缺陷,支持 30 多种语言与自定义规则,默认在本地扫描、不上传代码。跨文件分析与 Pro 规则需登录。
semgrep/semgrep17.1k
Grype
CLI扫描容器镜像、文件系统目录与 SBOM 中的已知漏洞,覆盖主流 Linux 发行版软件包和多种语言依赖,支持按 EPSS、KEV 排序风险,也支持用 OpenVEX 过滤结果,适合在 CI 中做漏洞门禁。由 Anchore 官方维护。
anchore/grype13k
Codex Security
CLIOpenAI 官方安全 CLI 与 TypeScript SDK:扫描代码库,发现、验证并修复安全漏洞,还能起草 SECURITY.md 安全策略。需要 Node.js 22.13+、Python 3.10+,并登录 ChatGPT 或配置 API Key。
openai/codex-security11.1k
zizmor
CLICI/CD 配置的安全静态分析工具:找出 GitHub Actions 工作流中的模板注入、凭据泄露、权限过大等问题,也覆盖 Dependabot 与 pre-commit 配置,部分问题可自动修复。
zizmorcore/zizmor6.7k