
Grype
CLI扫描容器镜像、文件系统目录与 SBOM 中的已知漏洞,覆盖主流 Linux 发行版软件包和多种语言依赖,支持按 EPSS、KEV 排序风险,也支持用 OpenVEX 过滤结果,适合在 CI 中做漏洞门禁。由 Anchore 官方维护。

Grype
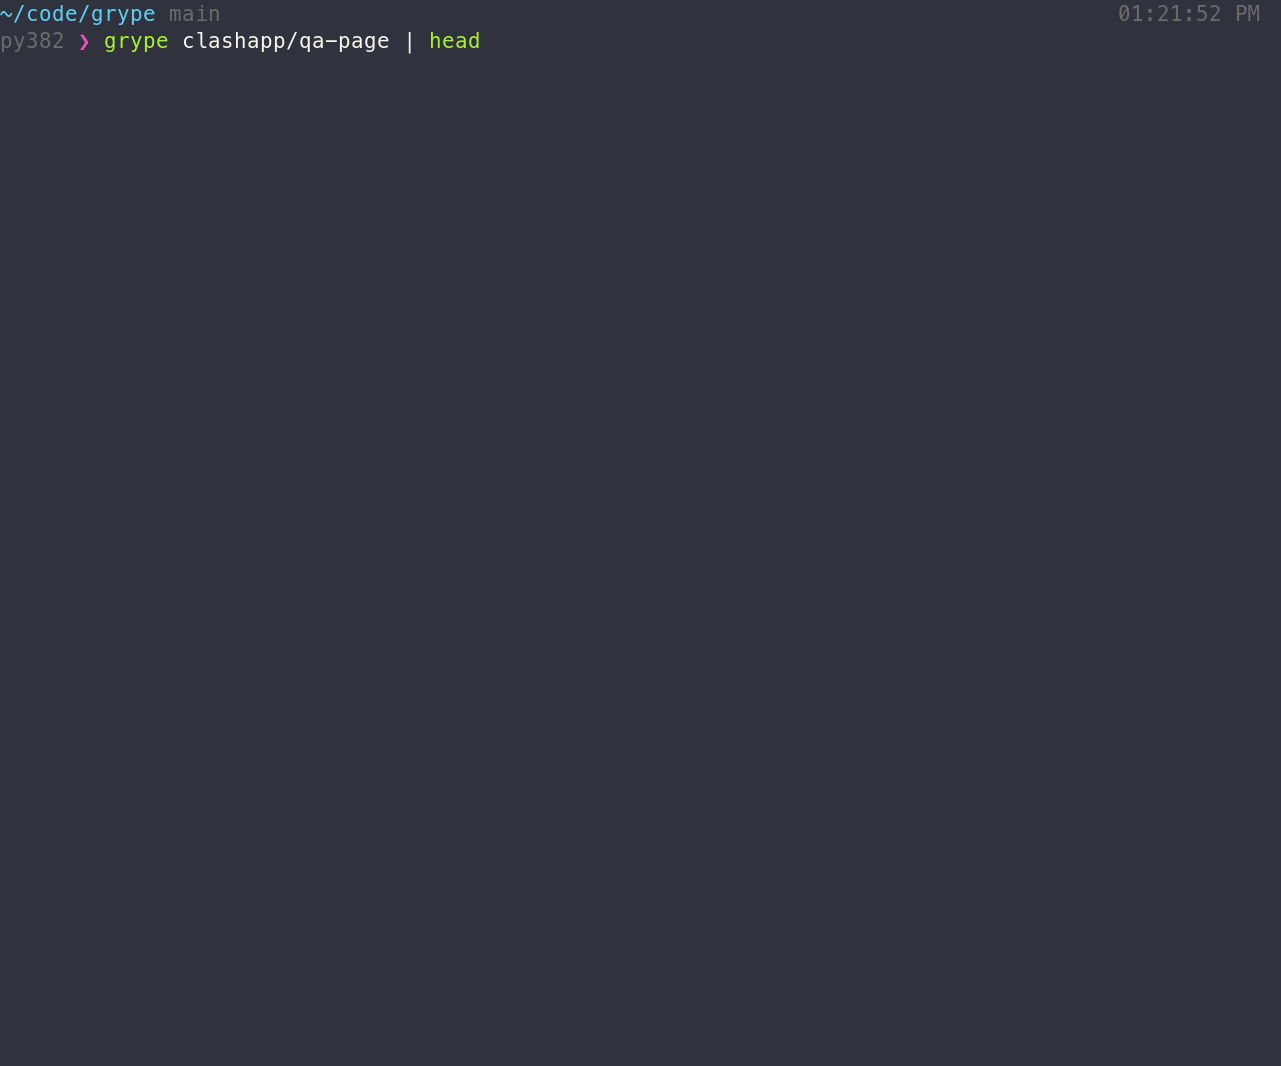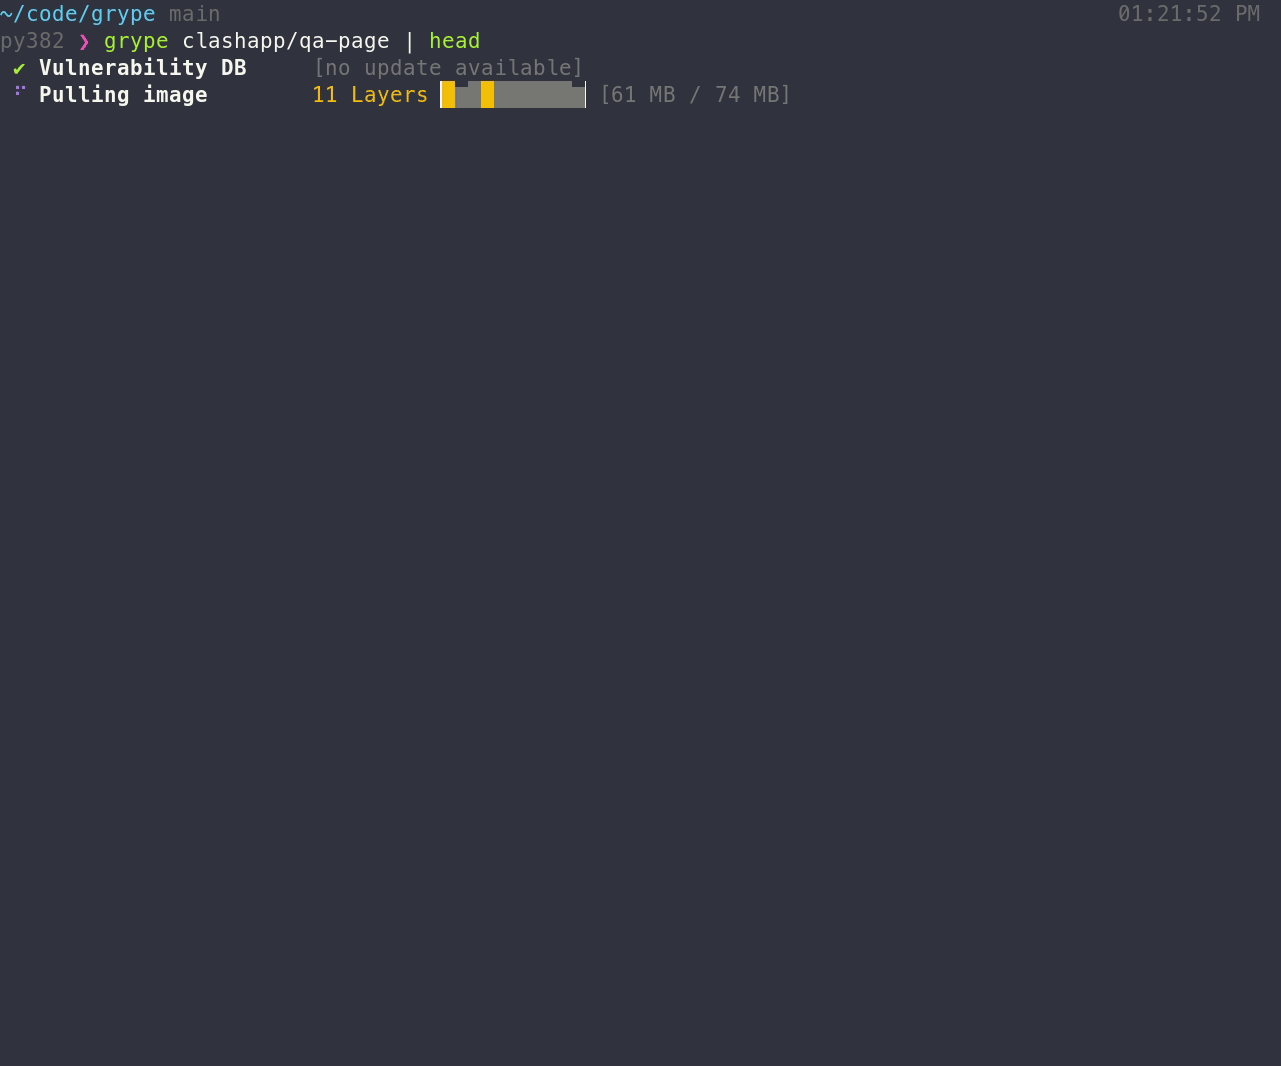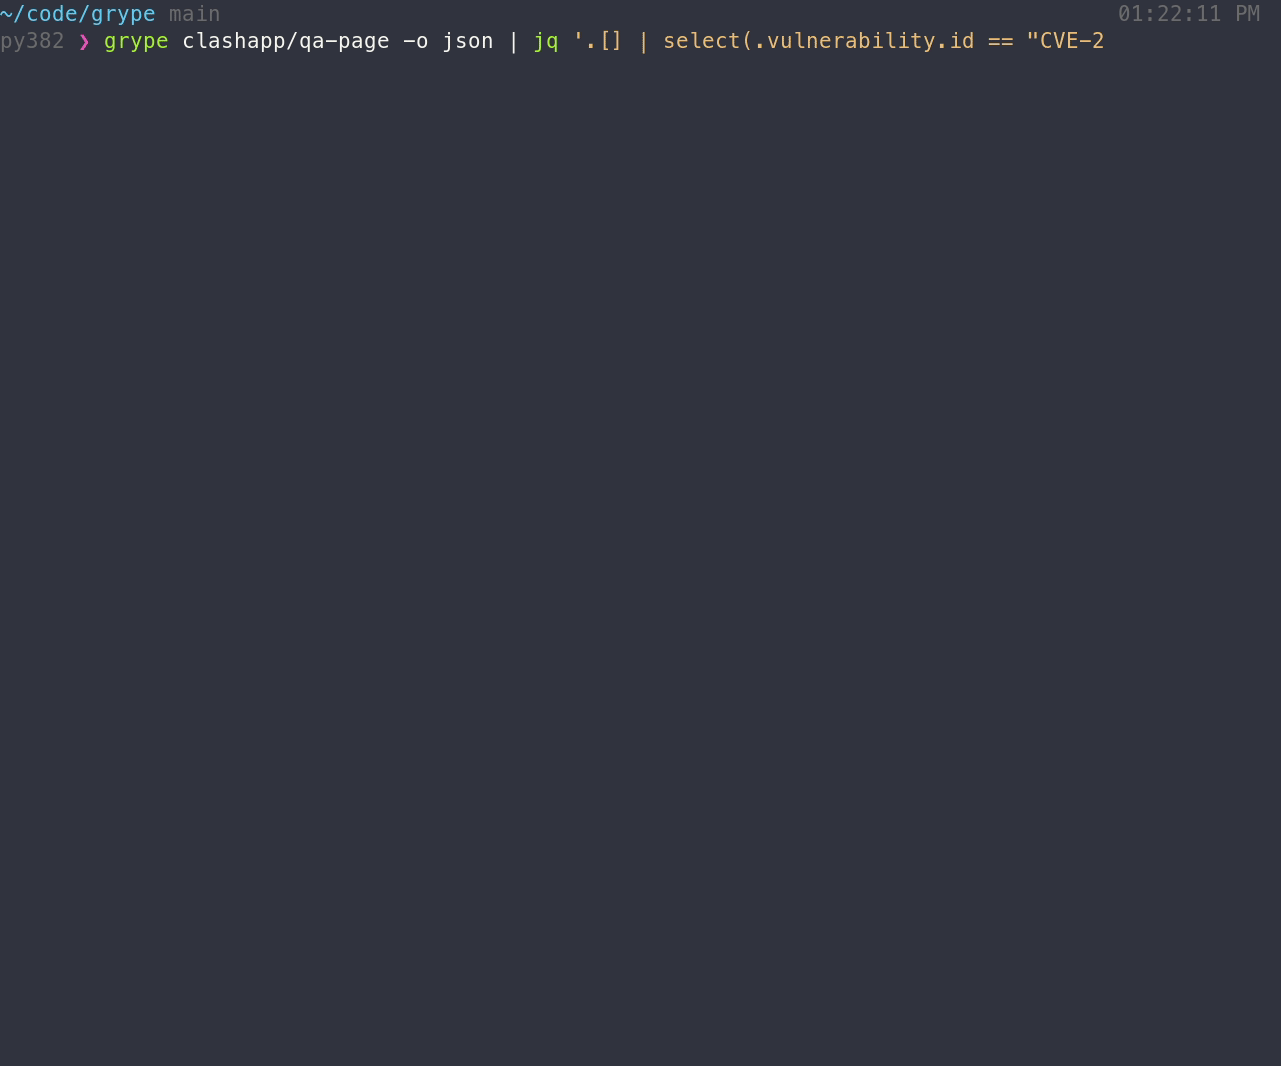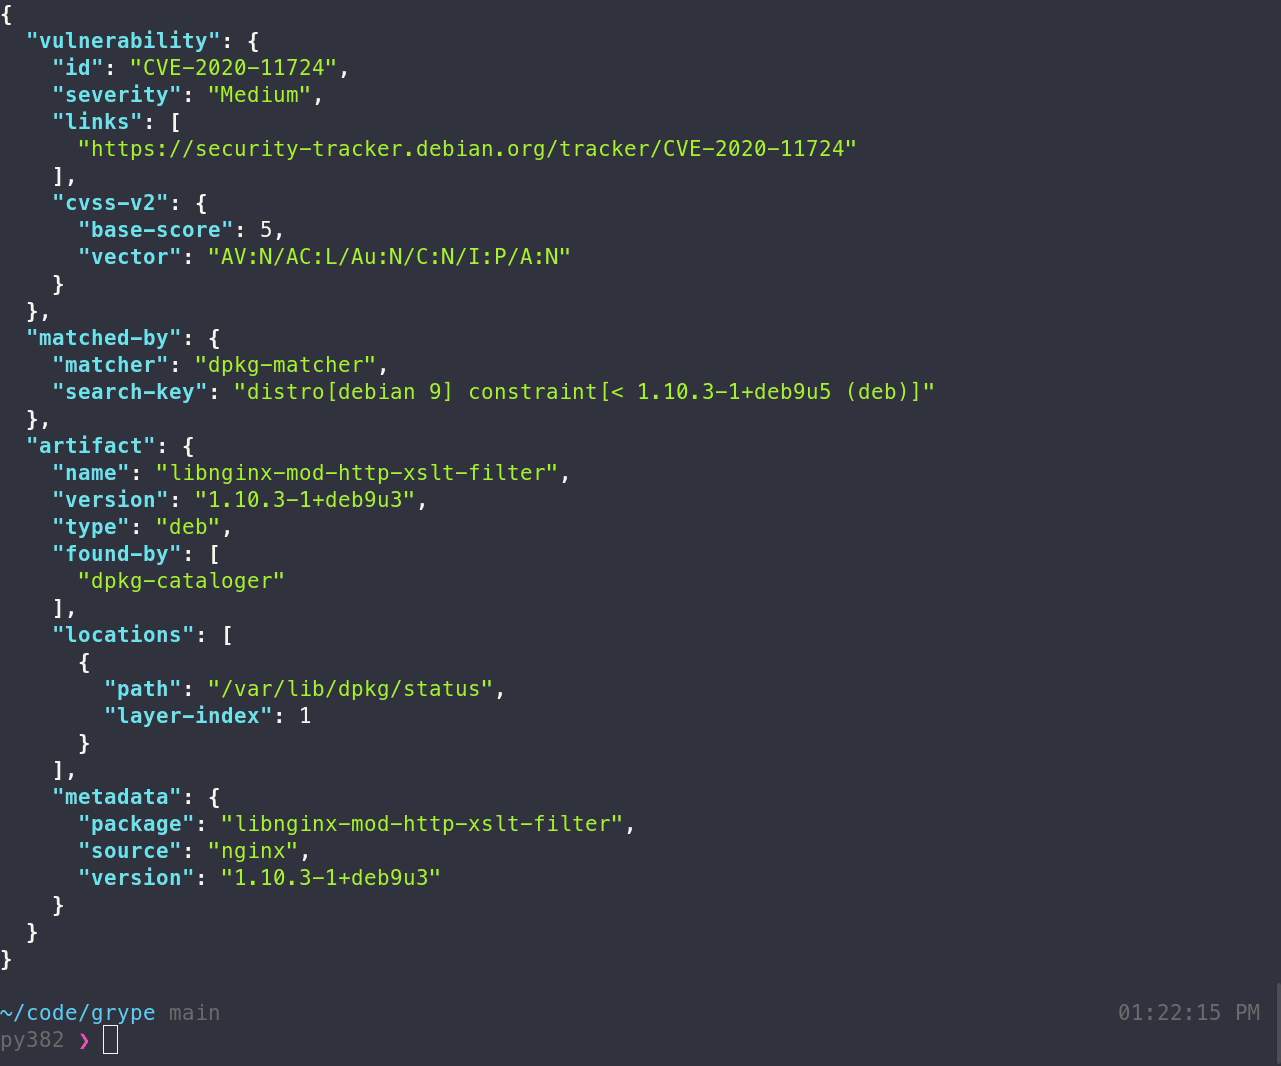
A vulnerability scanner for container images and filesystems.



Features
- Scan container images, filesystems, and SBOMs for known vulnerabilities (see the docs for a full list of supported scan targets)
- Supports major OS package ecosystems (Alpine, Debian, Ubuntu, RHEL, Oracle Linux, Amazon Linux, and more)
- Supports language-specific packages (Ruby, Java, JavaScript, Python, .NET, Go, PHP, Rust, and more)
- Supports Docker, OCI, and Singularity image formats
- Threat & risk prioritization with EPSS, KEV, and risk scoring (see interpreting the results docs)
- OpenVEX support for filtering and augmenting scan results
[!TIP] New to Grype? Check out the Getting Started guide for a walkthrough!
Installation
The quickest way to get up and going:
curl -sSfL https://get.anchore.io/grype | sudo sh -s -- -b /usr/local/bin
[!TIP] See Installation docs for more ways to get Grype, including Homebrew, Docker, Chocolatey, MacPorts, and more!
The basics
Scan a container image or directory for vulnerabilities:
# container image
grype alpine:latest

# directory
grype ./my-project
Local containers-storage images
On Linux, grype can scan images from a local containers-storage store (e.g. built with Buildah or Podman) when asked explicitly; plain image references never look there:
grype --from containers-storage localhost/myimage:latest

# rootless stores must be read from inside the builder's user namespace
podman unshare grype --from containers-storage localhost/myimage:latest
This is included in the Linux release binaries. When building from source, add -tags containers_image_openpgp,exclude_graphdriver_btrfs.
Scan an SBOM for even faster vulnerability detection:
# scan a Syft SBOM
grype sbom:./sbom.json

# pipe an SBOM into Grype
cat ./sbom.json | grype
[!TIP] Check out the Getting Started guide to explore all of the capabilities and features.
Want to know all of the ins-and-outs of Grype? Check out the CLI docs and configuration docs.
Contributing
We encourage users to help make these tools better by submitting issues when you find a bug or want a new feature. Check out our contributing overview and developer-specific documentation if you are interested in providing code contributions.
Grype development is sponsored by Anchore, and is released under the Apache-2.0 License.
The Grype logo by Anchore is licensed under CC BY 4.0

For commercial support options with Syft or Grype, please contact Anchore.
Come talk to us!
The Grype Team holds regular community meetings online. All are welcome to join to bring topics for discussion.
- Check the calendar for the next meeting date.
- Add items to the agenda (join this group for write access to the agenda)
- See you there!
相关资源

Trivy
CLI一站式安全扫描器:检查容器镜像、文件系统、Git 仓库与 Kubernetes 集群中的已知漏洞、IaC 错误配置、泄露密钥与软件许可证,并能生成 SBOM。Aqua Security 开源维护。
aquasecurity/trivy38.5k
OSV-Scanner
CLIGoogle 官方的依赖漏洞扫描器:解析项目的 lockfile 与容器镜像,对照 OSV.dev 漏洞库找出受影响的依赖,并可给出升级修复建议(实验功能)。
google/osv-scanner11.2kTrivy MCP Server
MCPTrivy 的 MCP 插件,让 agent 用自然语言扫描本地项目、容器镜像和远程仓库里的漏洞与配置错误,可选对接 Aqua 平台检查策略合规。需要先安装 Trivy,由 Aqua Security 官方维护。
aquasecurity/trivy-mcp53
Semgrep
CLI语义化的多语言静态分析工具:用写法接近源码的规则查找漏洞与缺陷,支持 30 多种语言与自定义规则,默认在本地扫描、不上传代码。跨文件分析与 Pro 规则需登录。
semgrep/semgrep17.1k
Dagger
CLI可编程的软件交付引擎:用 Go、Python、TypeScript 等 8 种语言的 SDK 编写构建、测试与发布流程,全部在容器中运行,本地与 CI 行为一致,自带 OpenTelemetry 追踪。需要 Docker 等容器运行时。
dagger/dagger16.3k
OSS Review Toolkit (ORT)
CLILinux 基金会旗下的开源合规工具链:分析软件项目的依赖,扫描许可证与版权信息并查询已知漏洞,按自定义策略标出违规项,生成 SBOM 与开源声明文件,便于法务和研发一起审查许可风险。需要 Java 25 或 Docker,建议 8GB 内存;许可证判定结果需法务人员复核。
oss-review-toolkit/ort2.1k