
Trivy
CLI一站式安全扫描器:检查容器镜像、文件系统、Git 仓库与 Kubernetes 集群中的已知漏洞、IaC 错误配置、泄露密钥与软件许可证,并能生成 SBOM。Aqua Security 开源维护。


Trivy (pronunciation) is a comprehensive and versatile security scanner. Trivy has scanners that look for security issues, and targets where it can find those issues.
Targets (what Trivy can scan):
- Container Image
- Filesystem
- Git Repository (remote)
- Virtual Machine Image
- Kubernetes
Scanners (what Trivy can find there):
- OS packages and software dependencies in use (SBOM)
- Known vulnerabilities (CVEs)
- IaC issues and misconfigurations
- Sensitive information and secrets
- Software licenses
Trivy supports most popular programming languages, operating systems, and platforms. For a complete list, see the Scanning Coverage page.
To learn more, go to the Trivy homepage for feature highlights, or to the Documentation site for detailed information.
Quick Start
Get Trivy
Trivy is available in most common distribution channels. The full list of installation options is available in the Installation page. Here are a few popular examples:
brew install trivydocker run aquasec/trivy- Download binary from https://github.com/aquasecurity/trivy/releases/latest/
- See Installation for more
Trivy is integrated with many popular platforms and applications. The complete list of integrations is available in the Ecosystem page. Here are a few popular examples:
- GitHub Actions
- Kubernetes operator
- VS Code plugin
- See Ecosystem for more
Canary builds
There are canary builds (Docker Hub, GitHub, ECR images and binaries) generated with every push to the main branch.
Please be aware: canary builds might have critical bugs, so they are not recommended for use in production.
General usage
trivy <target> [--scanners <scanner1,scanner2>] <subject>
Examples:
trivy image python:3.4-alpine
trivy fs --scanners vuln,secret,misconfig myproject/
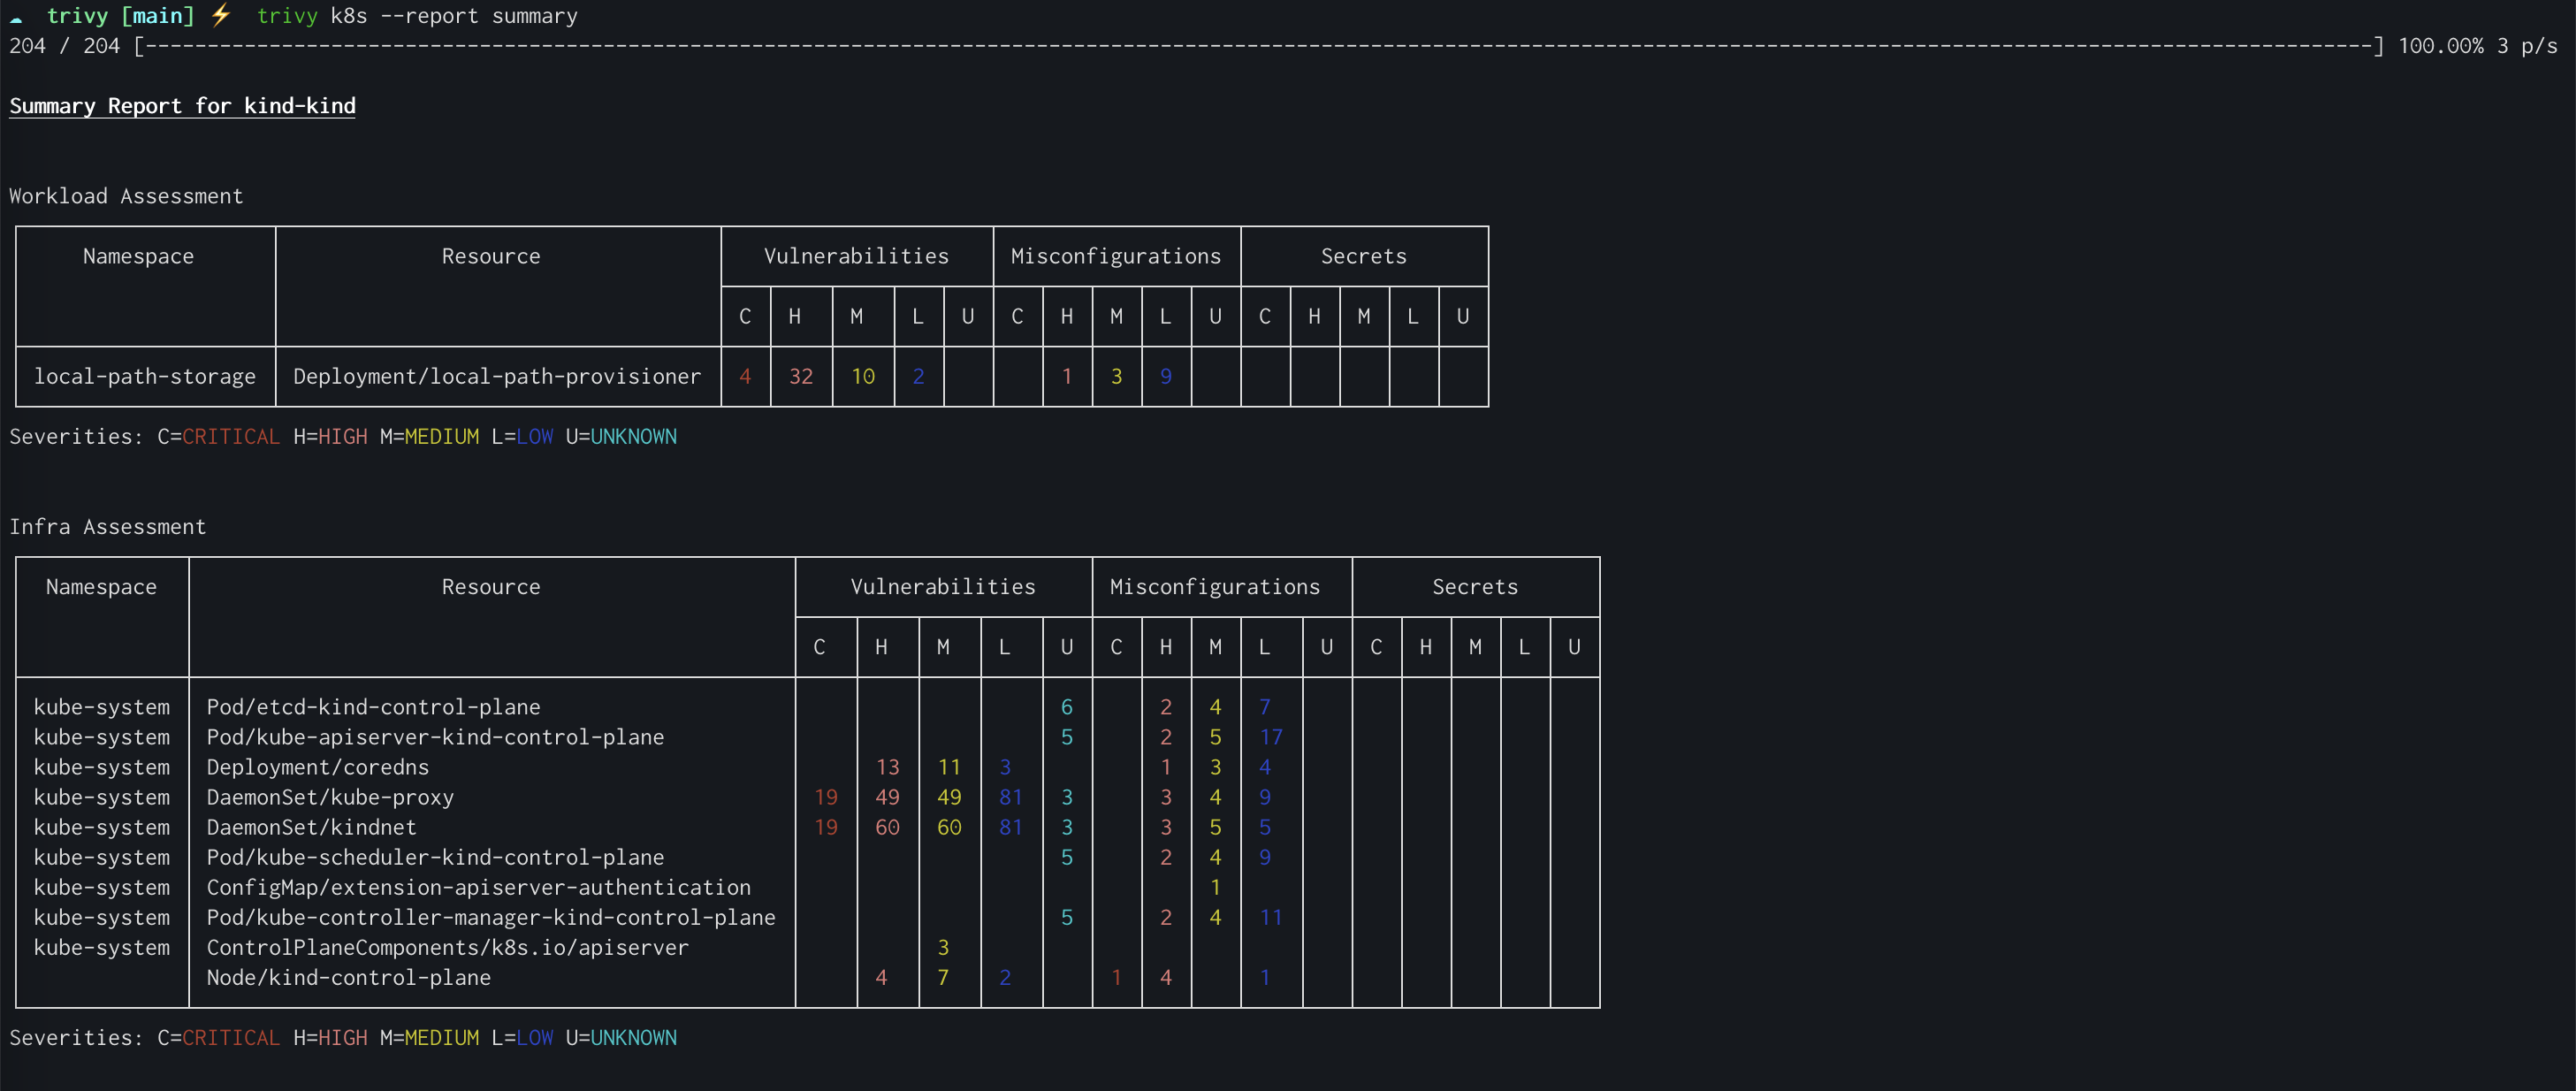
trivy k8s --report summary cluster
Result
FAQ
How to pronounce the name "Trivy"?
tri is pronounced like trigger, vy is pronounced like envy.
Want more? Check out Aqua
If you liked Trivy, you will love Aqua which builds on top of Trivy to provide even more enhanced capabilities for a complete security management offering.
You can find a high level comparison table specific to Trivy users here.
In addition check out the https://aquasec.com website for more information about our products and services.
If you'd like to contact Aqua or request a demo, please use this form: https://www.aquasec.com/demo
Community
Trivy is an Aqua Security open source project.
Learn about our open source work and portfolio here.
Contact us about any matter by opening a GitHub Discussion here
Please ensure to abide by our Code of Conduct during all interactions.
相关资源

Grype
CLI扫描容器镜像、文件系统目录与 SBOM 中的已知漏洞,覆盖主流 Linux 发行版软件包和多种语言依赖,支持按 EPSS、KEV 排序风险,也支持用 OpenVEX 过滤结果,适合在 CI 中做漏洞门禁。由 Anchore 官方维护。
anchore/grype13k
Checkov
CLI静态扫描 Terraform、CloudFormation、Kubernetes、Helm、Dockerfile 以及 CI 流水线配置里的安全和合规问题,内置上千条策略,能识别硬编码密钥,可输出 SARIF、JSON 等格式。由 Prisma Cloud 维护。
bridgecrewio/checkov9.1k
OSV-Scanner
CLIGoogle 官方的依赖漏洞扫描器:解析项目的 lockfile 与容器镜像,对照 OSV.dev 漏洞库找出受影响的依赖,并可给出升级修复建议(实验功能)。
google/osv-scanner11.2kTrivy MCP Server
MCPTrivy 的 MCP 插件,让 agent 用自然语言扫描本地项目、容器镜像和远程仓库里的漏洞与配置错误,可选对接 Aqua 平台检查策略合规。需要先安装 Trivy,由 Aqua Security 官方维护。
aquasecurity/trivy-mcp53
OSS Review Toolkit (ORT)
CLILinux 基金会旗下的开源合规工具链:分析软件项目的依赖,扫描许可证与版权信息并查询已知漏洞,按自定义策略标出违规项,生成 SBOM 与开源声明文件,便于法务和研发一起审查许可风险。需要 Java 25 或 Docker,建议 8GB 内存;许可证判定结果需法务人员复核。
oss-review-toolkit/ort2.1k
Docker Compose
CLI用 compose.yaml 定义多容器应用,一条 docker compose up 拉起服务、数据库、缓存等整套环境,适合 agent 搭建本地开发与测试依赖。Docker 官方维护,macOS 随 Docker Desktop 附带。
docker/compose38.4k